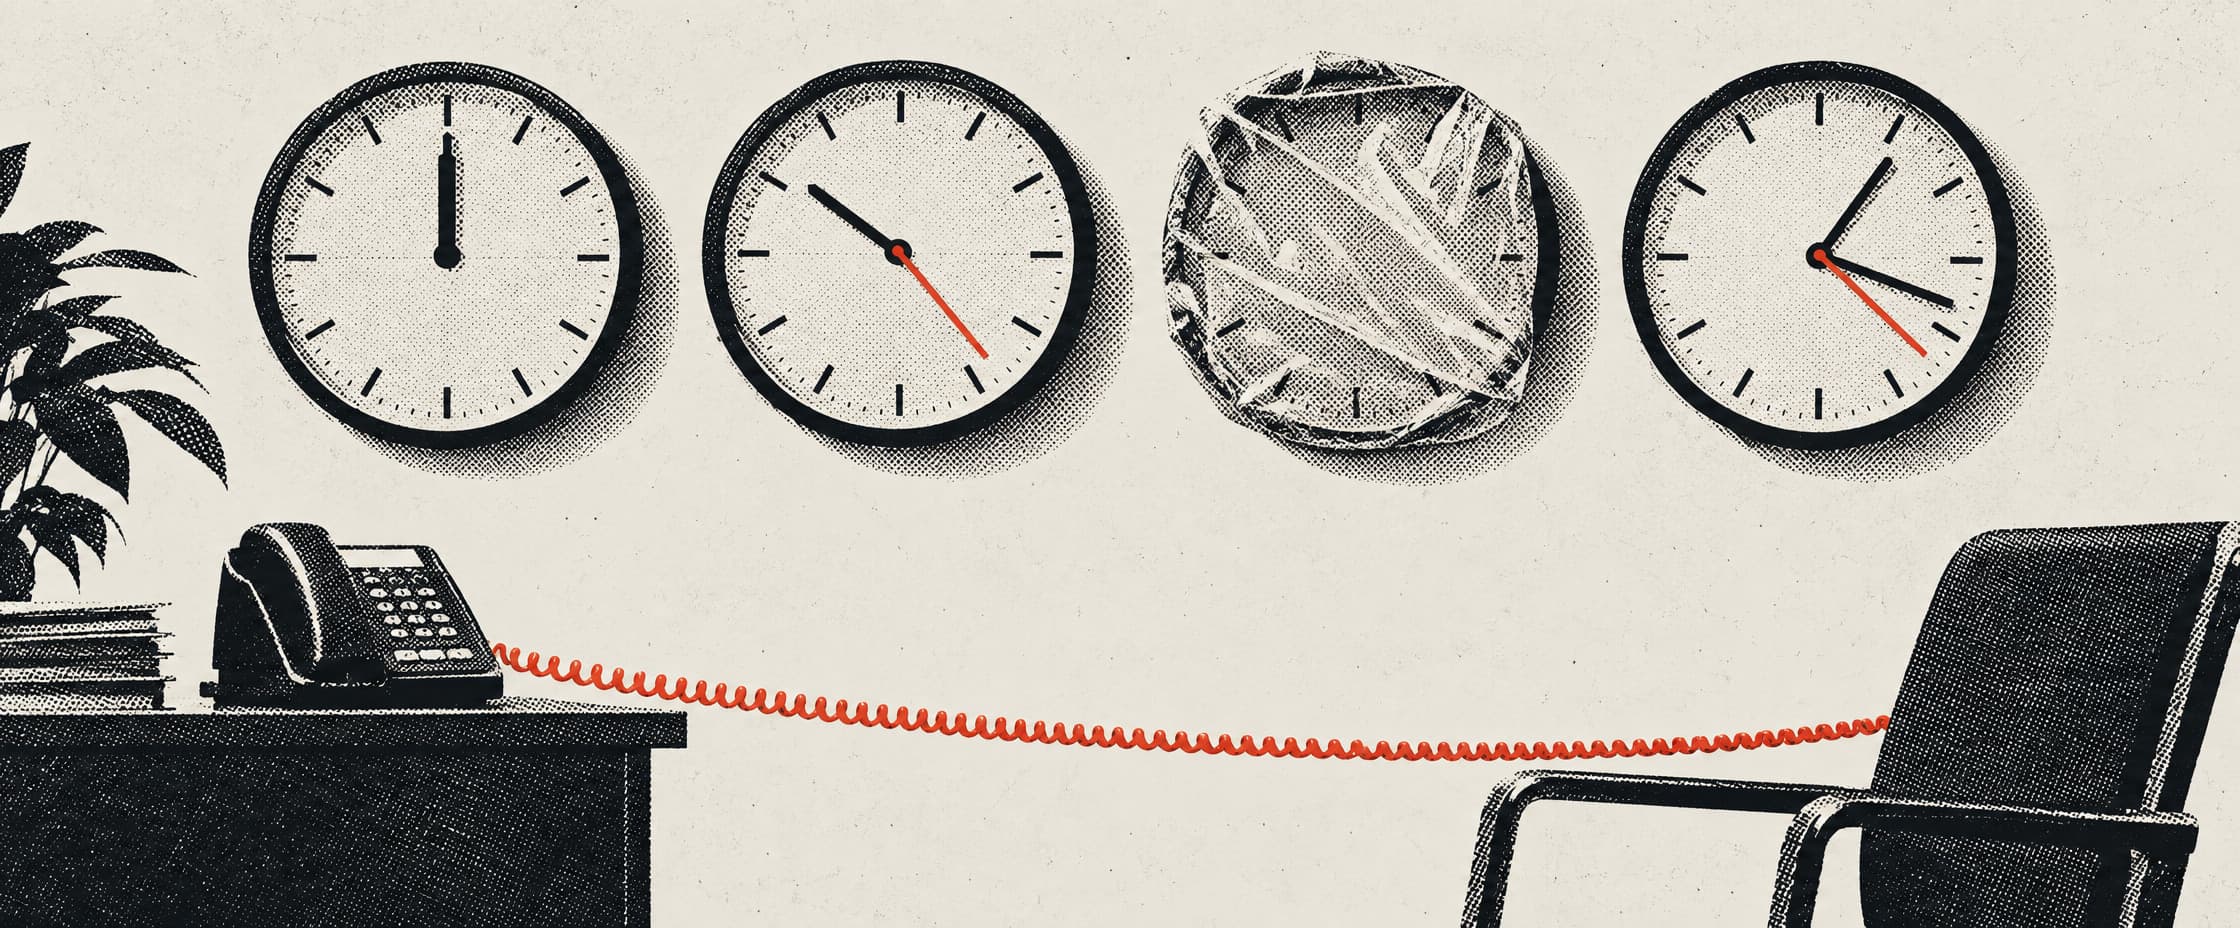
Four clocks, one incident. At a financial entity two of them are not running, and the fastest starts when somebody decides.
DORA's first report is due four hours after an incident is classified as major and never later than a day after anyone knew. The GDPR's seventy-two hours start from a different moment, and the person who owns that moment is usually in another meeting.
Draft, not yet edited. Written by Matteo Ferri, and not yet through the desk: nothing here has been checked against the sources listed at the foot of the page. Do not act on it.
At 09:40 on a Tuesday the payments API starts answering slowly. At 11:15 the security team confirms it is not slow, it is occupied: somebody got in through a supplier's remote-access account and has been reading the customer database. At 14:30 a committee agrees the incident is major. At 16:00 the DPO, who was told at 15:40, is satisfied that personal data have left the building.
Four timestamps, and every one of them starts something. The four European notification regimes that can apply to one incident at a regulated financial entity do not measure from the same moment, do not report to the same authority, and do not end on the same day. The popular version, four clocks started at once, is wrong in two directions. For most financial entities one of the four is switched off by law. For most of them another has not started yet. The two that remain start at different times and finish, with some regularity, on the same Friday afternoon.
What this procedure does, and where it stops
It gives you one sheet that says, for each regime, who is told, from which trigger, by when, and with what. It is written for a mid-sized financial entity in the scope of DORA, Regulation (EU) 2022/2554, with a group that may contain companies that are not.
It does not decide whether your incident is major. That is a judgement against thresholds, and step three shows you where the thresholds are, not how your services score against them. It does not cover national additions, law enforcement, insurers, contractual notice owed to counterparties, or disclosure duties for listed issuers, none of which I have checked for this piece. And it does not make the incident smaller. It stops you missing a deadline while the incident is being handled, which is a different problem with the same symptom on the regulator's side.
The four clocks, on one page
| Regime | Who is told | Clock starts at | What is due, and when | Runs for a DORA financial entity? |
|---|---|---|---|---|
| DORA, Article 19 and RTS 2025/301 | Your competent authority, via its secure channel | Classification as major, capped by awareness | Initial: four hours from classification, never later than 24 hours from awareness. Intermediate: 72 hours from the initial. Final: one month from the latest intermediate | Yes |
| NIS2, Article 23 | The CSIRT or competent authority | Awareness of a significant incident | Early warning: 24 hours. Notification: 72 hours. Final: one month from the notification | No, for the financial entity itself. Possibly for other group companies |
| GDPR, Articles 33 and 34 | The data protection authority; data subjects if high risk | Awareness of a personal data breach | 72 hours "where feasible", unless unlikely to result in a risk. Data subjects: without undue delay | Yes, alongside DORA |
| AI Act, Article 73 | Market surveillance authority, via the provider | Awareness of a serious incident | 15 days; two days for critical infrastructure or a widespread infringement; ten days for a death | Not for Annex III systems before 2 December 2027, on our reading |
Two things on that table are not what the briefing papers say.
The first is NIS2. Recital 16 of DORA calls the regulation "lex specialis" with regard to the directive, and Article 1(2) makes it a sector-specific act for the purposes of NIS2 Article 4. Article 4 then does the work: where a sector act imposes incident reporting at least equivalent in effect, the NIS2 provisions "shall not apply" to those entities. NIS2's own recital 28 says the same thing in plainer words. So the bank does not file an NIS2 early warning. Its DORA reports reach the NIS2 bodies anyway, because DORA Article 19(6)(c) obliges the competent authority to pass them on, and Article 19(1) lets a Member State require the bank to send copies to the CSIRT directly. That is a routing question for national law, not a second clock.
The second is the AI Act, which the next section deals with, because the answer is stranger than yes or no.
Before you start, and how long this really takes
You need four facts, and none of them can be found at 11:15 on the day.
The list of legal entities in the group, and against each one: is it a DORA financial entity, is it itself an essential or important entity under NIS2, and in which Member State. The secure channel your competent authority uses, working credentials for two people, and the fallback means you have agreed with the authority, because Article 4 of the implementing regulation, 2025/302, lets you use "other secure means" only in agreement with it. The data protection authority's breach form. And the name of whoever can say, before lunch, whether a high-risk AI system is in the path of the incident.
If reporting is outsourced to a service provider, Article 6 of 2025/302 required you to tell the authority before the first notification. Check that it was done.
Time: an afternoon to build the sheet if the group has one regulated entity and the DPO sits near the CISO. A fortnight if nobody has yet asked which group company is an NIS2 entity, because that question has an owner in legal and another in compliance, and they will each assume it is the other.
The steps
1. Open the incident log at detection, and write the time. Everything later is measured from a moment you will have to prove. The DORA initial notification must state the date and time of detection and of classification, under Article 2(b) of Delegated Regulation 2025/301.
2. Record awareness separately for each regime. They are different questions with different owners. DORA and NIS2 ask when you became aware of the incident. The GDPR asks when you became aware of a personal data breach, and the European Data Protection Board reads that as the point at which you have "a reasonable degree of certainty" that personal data were compromised, after a short investigation that must start at once (Guidelines 9/2022, paragraphs 31 and 34). In the Tuesday example that is 11:15 for DORA and 16:00 for the GDPR. The trap: the DPO's clock starts from what the controller knew, not from when the DPO was told, so an hour's delay in the corridor is spent from the DPO's seventy-two.
3. Classify under DORA, and write down the time you did. Delegated Regulation 2024/1772, Article 8: an incident is major if it has affected critical services and either meets the data-loss threshold in Article 9(5)(b) or meets two or more of the other thresholds. Article 9(5)(b) is met by any successful, malicious and unauthorised access to network and information systems that may result in data losses. So a confirmed intrusion into a system behind a critical service is major on its own, and the argument about client percentages can wait. The other thresholds include more than 10% of the service's clients, more than 100,000 clients, more than two hours of downtime for services supporting critical or important functions, and costs likely to exceed EUR 100,000. The classification time starts the fastest clock in this piece.
4. Send the DORA initial notification. Article 5(1)(a) of 2025/301: within four hours of classification and no later than 24 hours from awareness. Read those together. Classify at hour twenty-two and you have two hours, not four. If classification only happens after the first 24 hours, Article 5(2) gives you four hours from then. Use the Annex I template of 2025/302; fill the fields Article 2 of 2025/301 requires; estimate where you cannot measure, which Article 1(3) of 2025/302 permits. If you will miss the deadline, tell the authority before it passes, with reasons (Article 5(3)). The weekend rule, noon on the next working day, does not apply to an initial notification from a credit institution, a central counterparty, a trading venue operator or any financial entity identified as essential or important under NIS2 (Article 5(5)). A bank's Saturday is a Tuesday.
5. Decide the GDPR notification on its own terms. Article 33(1): notify the supervisory authority without undue delay and, where feasible, within 72 hours of awareness, unless the breach is unlikely to result in a risk to people. The minimum content is in Article 33(3); Article 33(4) lets you send it in phases. Past 72 hours, the notification must carry reasons for the delay. Every breach goes in the internal record under Article 33(5), notified or not. If the breach sits at a processor, Article 33(2) only requires them to tell you without undue delay, which is why the contract should say something sharper.
6. Tell the customers, under two duties that are not the same duty. DORA Article 19(3): where a major incident affects clients' financial interests, inform them without undue delay of the incident and of the measures taken. GDPR Article 34: where a breach is likely to result in a high risk, tell the data subjects without undue delay, in clear and plain language, with the content listed in Article 33(3)(b) to (d). One letter can do both only if it carries both sets of content. Neither has a number of hours, and "without undue delay" is not a licence to wait for the intermediate report.
7. Check NIS2 for every group company that is not a DORA financial entity. If the intrusion came through the group's own IT services company and that company is itself an essential or important entity, its clock is Article 23(4): early warning within 24 hours of becoming aware of a significant incident, a notification within 72 hours, a final report no later than one month after the notification. The trap is in the last one: one month from the notification, not from the incident. Which of your group companies are in scope is a question for the register before the incident, not for the log during it. I have not checked the NIS2 annex against any particular group structure, and this page does not answer it for you.
8. Ask whether a high-risk AI system is involved, and then read the date. Article 73 of the AI Act makes providers of high-risk systems report serious incidents to market surveillance authorities: within 15 days of awareness, two days for a serious disruption of critical infrastructure or a widespread infringement, ten days after a death. A deployer, which is what a bank buying a credit-scoring model is, must "immediately inform first the provider" under Article 26(5). Annex III, point 5, names creditworthiness assessment and life and health insurance pricing, so the question is live for most readers.
The date is not. The Digital Omnibus on AI, Regulation (EU) 2026/1744, in force since 27 July, moved Chapter III, Sections 1 to 3, to 2 December 2027 for Annex III systems. That chapter holds the classification rules and the deployer duties. Article 73 sits in Chapter IX and was not moved. So the reporting duty has applied since 2 August 2026 and the rules that say which systems it applies to have not. Our reading is that no Article 73 clock runs for an Annex III system before December 2027. We could not find guidance that confirms it, and a firm that reports anyway is not wrong.
When it does run, Article 73(9) limits providers already under equivalent Union reporting to one category of serious incident, the infringement of obligations protecting fundamental rights. Whether DORA counts as equivalent for a financial entity that builds its own model is a question nobody has answered in a way that survives a follow-up.
9. Before you leave on Tuesday, diary the follow-ups. The DORA intermediate report is due within 72 hours of the initial notification, "even where the status or the handling of the incident have not changed", and again when regular activities recover. The final report is due one month after the latest intermediate report, so every update you file moves it. Two or three reports can be filed together if the time limits are still met (2025/302, Article 2).
DORA, the financial entityinitial due 18:30, four hours after classification
GDPR, the controlleraware at 16:00
NIS2, the group IT companyonly if it is itself in scope
AI Act, Annex III systemon our reading
How to tell it worked
The log has, for each regime that applied, four entries: the trigger and its time, the deadline you computed from it, the time you submitted, and the acknowledgement. DORA Article 22(1) obliges the competent authority to acknowledge receipt, so an initial notification without an acknowledgement is a notification you should chase before assuming it arrived.
The better test is before the incident. Run the Tuesday above as a tabletop with the CISO, the DPO and whoever signs for DORA reporting in the same room, and have each compute their deadlines independently. If the three answers disagree, you have found the gap more cheaply than the regulator would have.
How to undo it
You cannot unsend a notification, and none of these texts pretends otherwise.
Under DORA, if further assessment shows the incident at no time met the Article 8 criteria, Article 5 of 2025/302 lets you reclassify it from major to non-major, using the template. "At no time" is the operative phrase. An incident that was major and has stopped being major is not reclassified; it is resolved, and the final report still follows.
The GDPR has no withdrawal mechanism in its text. What it has is phased information under Article 33(4), which is the route for saying that the risk assessment has changed. I could find nothing in the regulation that treats a notification made in caution as a failing.
If a deadline is about to be missed, the reversal is to say so before it passes. DORA requires it (2025/301, Article 5(3)); the GDPR requires reasons with a late notification. A late report with an explanation filed on time is a different conversation from a late report the authority discovers.
What comes next
The Commission's digital omnibus proposal on data and cyber rules would, as reported, raise the GDPR notification threshold to high risk, extend the 72 hours to 96, and create a single entry point for incident reports under several instruments including DORA and NIS2. It has been reported as awaiting a committee decision in the Parliament over the summer. None of it is law, and I have not read the proposal, so the sheet does not change on its account.
The date that does change the sheet is 2 December 2027, when the fourth clock gets the definition it currently lacks. Until then, the clocks that actually run at a financial entity are two, set by a committee's decision and a DPO's certainty. Which of those comes first on your Tuesday is the one thing worth rehearsing.
Written from
Primary The document itself. Claims in this piece rest only on these.
- Regulation (EU) 2022/2554 on digital operational resilience for the financial sector (DORA)Opened for this piece, from the Publications Office's own copy of the Official Journal text. Read: recitals 15 and 16, Article 1(2), Article 18, Article 19 in full, Article 20, Article 22(1). Source for: the classification criteria; the duty to report major incidents to the competent authority; the three-stage initial, intermediate and final structure; the rule that the final report follows completion of the root cause analysis; the duty to inform clients whose financial interests are affected 'without undue delay'; the option for Member States to require copies to NIS2 authorities or CSIRTs; onward transmission by the competent authority to NIS2 bodies; the acknowledgement of receipt; and the statement that DORA is lex specialis to NIS2 and a sector-specific act for the purposes of NIS2 Article 4. DORA itself sets no hours. The hours come from the delegated regulation below.
- Commission Delegated Regulation (EU) 2025/301, RTS on the content and time limits for the initial notification of, and intermediate and final report on, major ICT-related incidentsRead in full. Source for every DORA time limit printed here: Article 5(1)(a), initial notification within four hours of classification as major and no later than 24 hours from awareness; Article 5(2), four hours from a classification made after the first 24 hours; Article 5(1)(b), intermediate report within 72 hours of the initial notification even if nothing has changed, and an updated one when regular activities have recovered; Article 5(1)(c), final report no later than one month after the latest intermediate report; Article 5(3), informing the authority before a missed deadline; Article 5(4) to (6), the weekend and bank-holiday rule and who is excluded from it. Also Articles 1 and 2 for the content of the initial notification.
- Commission Implementing Regulation (EU) 2025/302, ITS on the standard forms, templates and procedures for reporting a major ICT-related incidentRead Articles 1 to 7. The annexes, which hold the template and the data glossary, were not read field by field. Source for: estimates being permitted where accurate data are not yet available; joint submission of two or three reports at once; use of the authority's secure electronic channel and the fallback to other secure means; reclassification from major to non-major; the duty to tell the authority in advance if reporting is outsourced.
- Commission Delegated Regulation (EU) 2024/1772, RTS on the classification of ICT-related incidents and cyber threats and materiality thresholdsRead Articles 8 and 9 closely, Articles 1 to 7 for their headings and structure only. Source for the major-incident test: critical services affected, plus either the data-loss threshold in Article 9(5)(b) or two or more of the other thresholds; and for the thresholds quoted in step three.
- Directive (EU) 2022/2555 (NIS2)Opened for this piece. Read: recital 28, Article 4 and Article 23 in full, Article 2(10) and (12). Source for: the early warning within 24 hours, the incident notification within 72 hours and the final report within one month of the notification, all measured from becoming aware of a significant incident; the definition of significant; and the rule that where a sector-specific act such as DORA imposes equivalent reporting, the NIS2 reporting provisions do not apply to those entities. The Annex I list of sectors was not reread for this piece; the body therefore makes no claim about which non-financial group companies fall within NIS2 and says so. National transposition laws were not opened.
- Regulation (EU) 2016/679 (GDPR), Articles 33 and 34Read Articles 33 and 34 in full. Source for the 72 hours from awareness 'where feasible', the exemption where a breach is unlikely to result in a risk, the reasons for delay, the minimum content, information in phases, the processor's duty to tell the controller, the internal record of every breach, and the high-risk test and exemptions for telling data subjects.
- EDPB Guidelines 9/2022 on personal data breach notification under GDPR, version 2.0Read paragraphs 31 to 35. Source for the reading of 'aware' as a reasonable degree of certainty that personal data have been compromised, and for the short period of investigation before that point. Guidance, not law, and the body says so.
- Regulation (EU) 2024/1689 (AI Act), as publishedRead Article 3(49), Article 26(5), Article 73 in full, Article 113 and Annex III point 5. Source for the 15-day, two-day and ten-day limits, the deployer's duty to inform the provider 'immediately', the limitation in Article 73(9) for providers already under equivalent Union reporting, and the Annex III entries on creditworthiness and on life and health insurance pricing. The consolidated text as amended in 2026 was not opened; the amendments were read in the amending act below.
- Regulation (EU) 2026/1744 amending Regulation (EU) 2024/1689 (Digital Omnibus on AI)Opened and searched, not read end to end. Source for the new Article 113 wording: Chapter III, Sections 1 to 3, apply from 2 December 2027 for Annex III systems and 2 August 2028 for Annex I systems. The body's conclusion that no Article 73 clock runs for an Annex III system before December 2027 is this desk's reading of how that date meets Article 73, which sits in Chapter IX and was not moved. The body labels it a reading. No guidance confirming or contradicting it was found.
- Commission guidelines on the application of NIS2 Article 4 (sector-specific acts)Not opened. NIS2 Article 4(3) required them by 17 July 2023. Nothing in the body rests on them; the lex specialis point is sourced to the two instruments themselves.
Reporting Attributed, not relied on. Where the reporting is the fact, it says so.
- Legislative status of the Commission's Digital Omnibus proposal on data and cyber rules (GDPR breach threshold and 96 hours; single entry point for incident reports)Not opened. The proposal's text, number and article references were not read for this piece, and none is printed. Its status, awaiting a Parliament committee decision as of summer 2026, comes from secondary coverage found by search and is attributed in the body as reported, not as fact.